Business
Countering cyber crime
There are many precautions individuals and businesses can take to prevent online scams
"The single biggest factor for these scams is the negligence of its employees or lapse in human judgment,” wrote Mehrzaad Mogrelia (pictured) who ran his own venture, MZ Consultancy (mehrzaadmogrelia@gmail.com) to help companies unearth financial frauds. He has recently taken up an assignment in Canada. He has been featured in the list of Top 30 Under 30 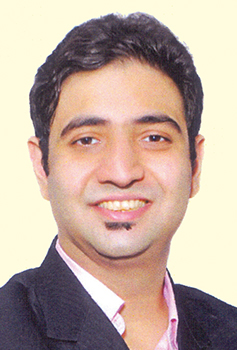 Emerging Industry Experts in financial crime prevention by Business Mint. Even the top technology companies such as Microsoft, Facebook and Google can be victims of scams, pointed out the financial crime specialist. Parsiana had sought his reaction to recent cyber scams on three prominent Parsi run organizations.
An innocuous email arrived in the Parsiana mail box on September 20, 2022, titled "Touching base.” Purportedly from an ex-interviewee based in the USA, industrialist Farrokh Patel, it asked innocently, "I want to know if this email address is still valid to write to you. There is something important I would like to discuss with you.” When Parsiana responded that it was the right address, the next mail inquired whether we had an Amazon account. It was only after this second mail was responded to in the affirmative, did it emerge that Patel’s account had been hacked. Patel stated, "The hackers sent out emails to every one of my associates that I wanted money from them… All my friends knew better and I put a stop to that … I have changed my email address.”
Six days, later, in an unrelated incident, the Facebook account of chairman of the World Zoroastrian Organisation Trusts was "hacked and seized.” The hacker took control of the account, according to trustee Freyaz Shroff. "The WZO Trust Funds pages have also been compromised and currently marked for deletion in 14 days” by Facebook, after she lodged a complaint with the platform, noted Shroff. "We have rarely used Facebook to solicit funds, so donors may not respond if mails soliciting funds are sent out by the hacker.”
These incidents come on the heels of an impostor defrauding the mega company Serum Institute of India of one crore rupees by posing as the chief executive officer Adar Poonawalla. Reportedly, a scammer sent a WhatsApp message as if from Poonawalla’s number to SII director Satish Deshpande asking for money transfers. The latter instructed finance manager Sagar Kittur "to follow the instructions for online transfers to different accounts supplied by the ersatz Poonawalla… Later the accounts office realized the company had been cheated” (The Free Press Journal, September 11, 2022). A case of cyber fraud and cheating has been filed.
The "human” factor that could lead to frauds often goes unnoticed. "This can be partly due to the lack of training in areas like detection of phishing (the practice of sending emails purporting to be from reputed companies to induce people to reveal personal information), data security measures or the employee treating the training lightly,” Mogrelia stated. It is a combination of technology and people that make a business system secure, rather than a single factor, he pointed out.
 As soon as businesses introduce new technology or security measures, it is necessary to train employees on their features, how they work and their end use. "Without the right training, what would have been a boon for the company will soon become a bane and (could) lead to losses including scammers attacking the information technology system and confidential data being compromised.” Mogrelia recommends periodic training.
Businesses need to ensure that all their data is backed up, either on a separate cloud platform not associated with their business accounts or on an external hard disk that is stored away securely. "Backup should be taken daily at the end of the working day to ensure that there is no data loss,” Mogrelia warned. Passwords should be changed periodically, say every 30 to 45 days, recommends the 27-year-old entrepreneur. Depending on complexity of operations, network capabilities must be constantly updated and new security measures introduced.
A special response plan to cyber-attacks should be designed, irrespective of the size of the organization, he emphasized. This plan must include names of members of the response team, their roles and responsibilities, protocols to be followed in case of an attack. A mock drill which includes employees identifying phishing emails or messages or a mock cyber-attack can be carried out to prepare everyone for the worst case scenario.
Mogrelia recommends businesses carry out a "Know your employee” exercise especially for those handling sensitive data. This can be done via searches over the internet and checks for criminal records and references. "On several occasions, it’s the employees rather than the external forces that cause data breaches.” He pointed out the example of a network engineer at oil company EnerVest Operating LLC in Charleston, USA, who caused intentional damage to the company’s network system after learning he was about to be fired!
"Email and social media communications have become an integral part of the modern day life… However, this has also become one of the most common mediums for cyber criminals to commit crimes like data theft, identity theft, online scams (job fraud, romance scam), laundering money from one place to another,” said Mogrelia. Thirty-six percent of data breaches involve the use of phishing emails according to a 2021 Data Breach Investigation Report by software giant Verizon, he stated, adding that 80% of targeted cyber crimes take place through web applications like Facebook, WhatsApp, Instagram, among others as per the Verizon report.
The cyber expert recommends some tips to keep users safe on social media: Keep an eye out for any irregularities in the sender’s name, email address or body of the letter. Irregularities like spelling mistakes, poorly constructed emails, strange email addresses that appear to be genuine, unrealistic offers are some of the major indicators that the email might not be genuine. "If a friend or family member has an ostensible emergency, we should cross-check by calling them up to know if the situation exists before transferring any funds to their Paypal or Paytm accounts,” he says. Avoid disclosing personal details on social media profiles in order to protect your profile and avoid leakage of confidential information.
The use of additional sign-in methods like fingerprint scan and facial scan, and security questions, besides passwords, provide additional security. "Nearly every email and social media platform offers the two-factor authentication feature which should definitely be enabled,” he avers. Avoid creating multiple profiles across social media platforms, Mogrelia advises. "While dedicated use of each profile, say for gaming or viewing streaming platforms might sound an amazing perspective, it is actually easy bait for cyber criminals to take over one profile and commit illicit activities under the individual’s identity.”
The first thing one should do after falling victim to a cyber crime is to report it via the online reporting platform of the Cyber Cell in the jurisdiction where the crime has occurred so that traces of the origin of the email/message and transaction trails can be connected, which could help nab the criminal much faster.
"With the right framework, guidelines and training, businesses can actually protect themselves from such scams to a large extent,” ended Mogrelia.
Emerging Industry Experts in financial crime prevention by Business Mint. Even the top technology companies such as Microsoft, Facebook and Google can be victims of scams, pointed out the financial crime specialist. Parsiana had sought his reaction to recent cyber scams on three prominent Parsi run organizations.An innocuous email arrived in the Parsiana mail box on September 20, 2022, titled "Touching base.” Purportedly from an ex-interviewee based in the USA, industrialist Farrokh Patel, it asked innocently, "I want to know if this email address is still valid to write to you. There is something important I would like to discuss with you.” When Parsiana responded that it was the right address, the next mail inquired whether we had an Amazon account. It was only after this second mail was responded to in the affirmative, did it emerge that Patel’s account had been hacked. Patel stated, "The hackers sent out emails to every one of my associates that I wanted money from them… All my friends knew better and I put a stop to that … I have changed my email address.”
Six days, later, in an unrelated incident, the Facebook account of chairman of the World Zoroastrian Organisation Trusts was "hacked and seized.” The hacker took control of the account, according to trustee Freyaz Shroff. "The WZO Trust Funds pages have also been compromised and currently marked for deletion in 14 days” by Facebook, after she lodged a complaint with the platform, noted Shroff. "We have rarely used Facebook to solicit funds, so donors may not respond if mails soliciting funds are sent out by the hacker.”
These incidents come on the heels of an impostor defrauding the mega company Serum Institute of India of one crore rupees by posing as the chief executive officer Adar Poonawalla. Reportedly, a scammer sent a WhatsApp message as if from Poonawalla’s number to SII director Satish Deshpande asking for money transfers. The latter instructed finance manager Sagar Kittur "to follow the instructions for online transfers to different accounts supplied by the ersatz Poonawalla… Later the accounts office realized the company had been cheated” (The Free Press Journal, September 11, 2022). A case of cyber fraud and cheating has been filed.
The "human” factor that could lead to frauds often goes unnoticed. "This can be partly due to the lack of training in areas like detection of phishing (the practice of sending emails purporting to be from reputed companies to induce people to reveal personal information), data security measures or the employee treating the training lightly,” Mogrelia stated. It is a combination of technology and people that make a business system secure, rather than a single factor, he pointed out.
As soon as businesses introduce new technology or security measures, it is necessary to train employees on their features, how they work and their end use. "Without the right training, what would have been a boon for the company will soon become a bane and (could) lead to losses including scammers attacking the information technology system and confidential data being compromised.” Mogrelia recommends periodic training. Businesses need to ensure that all their data is backed up, either on a separate cloud platform not associated with their business accounts or on an external hard disk that is stored away securely. "Backup should be taken daily at the end of the working day to ensure that there is no data loss,” Mogrelia warned. Passwords should be changed periodically, say every 30 to 45 days, recommends the 27-year-old entrepreneur. Depending on complexity of operations, network capabilities must be constantly updated and new security measures introduced.
A special response plan to cyber-attacks should be designed, irrespective of the size of the organization, he emphasized. This plan must include names of members of the response team, their roles and responsibilities, protocols to be followed in case of an attack. A mock drill which includes employees identifying phishing emails or messages or a mock cyber-attack can be carried out to prepare everyone for the worst case scenario.
Mogrelia recommends businesses carry out a "Know your employee” exercise especially for those handling sensitive data. This can be done via searches over the internet and checks for criminal records and references. "On several occasions, it’s the employees rather than the external forces that cause data breaches.” He pointed out the example of a network engineer at oil company EnerVest Operating LLC in Charleston, USA, who caused intentional damage to the company’s network system after learning he was about to be fired!
"Email and social media communications have become an integral part of the modern day life… However, this has also become one of the most common mediums for cyber criminals to commit crimes like data theft, identity theft, online scams (job fraud, romance scam), laundering money from one place to another,” said Mogrelia. Thirty-six percent of data breaches involve the use of phishing emails according to a 2021 Data Breach Investigation Report by software giant Verizon, he stated, adding that 80% of targeted cyber crimes take place through web applications like Facebook, WhatsApp, Instagram, among others as per the Verizon report.
The cyber expert recommends some tips to keep users safe on social media: Keep an eye out for any irregularities in the sender’s name, email address or body of the letter. Irregularities like spelling mistakes, poorly constructed emails, strange email addresses that appear to be genuine, unrealistic offers are some of the major indicators that the email might not be genuine. "If a friend or family member has an ostensible emergency, we should cross-check by calling them up to know if the situation exists before transferring any funds to their Paypal or Paytm accounts,” he says. Avoid disclosing personal details on social media profiles in order to protect your profile and avoid leakage of confidential information.
The use of additional sign-in methods like fingerprint scan and facial scan, and security questions, besides passwords, provide additional security. "Nearly every email and social media platform offers the two-factor authentication feature which should definitely be enabled,” he avers. Avoid creating multiple profiles across social media platforms, Mogrelia advises. "While dedicated use of each profile, say for gaming or viewing streaming platforms might sound an amazing perspective, it is actually easy bait for cyber criminals to take over one profile and commit illicit activities under the individual’s identity.”
The first thing one should do after falling victim to a cyber crime is to report it via the online reporting platform of the Cyber Cell in the jurisdiction where the crime has occurred so that traces of the origin of the email/message and transaction trails can be connected, which could help nab the criminal much faster.
"With the right framework, guidelines and training, businesses can actually protect themselves from such scams to a large extent,” ended Mogrelia.
◆ ◆ ◆
From the archive